“If you revoke the GitHub token it stole, a background job on your machine deletes your home directory.”
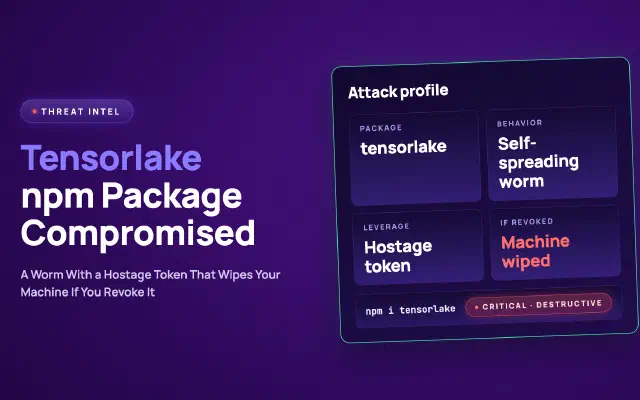
The standard incident response is now a trigger. Revoke the token first and you lose your home directory. The poisoned release carried a valid npm provenance attestation, so the supply chain checks everyone was told to trust signed off on it. Provenance proves where malware was built. That is all it proves.