“Linux’s stable kernels shipped a fix on October 11 and 15, 2026 for CVE-2026-98432, a use-after-free in the IPv4 TCP handshake that a remote, unauthenticated peer can reach.”
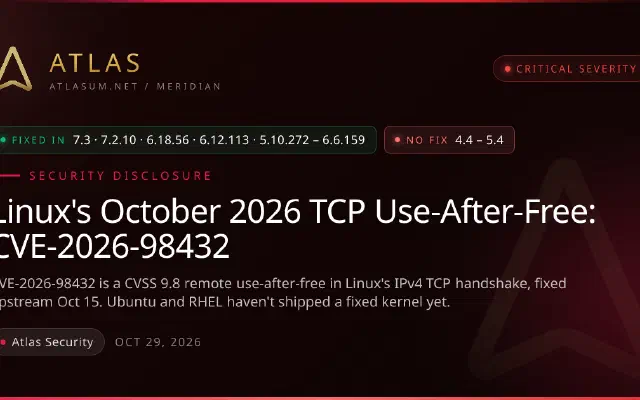
The bug reaches back to Linux 4.4 and needs no credentials. The upstream fix is four lines and shipped October 11. Twenty days later, Ubuntu still lists every release as vulnerable and Red Hat has no fix for RHEL 8, 9 or 10. Amazon Linux patched every kernel, so the delay is a choice.