“This simple tweak removes all the protection granted by the server-side iterations and speeds up master password guessing considerably. Only the client-side iterations really matter as protection.”
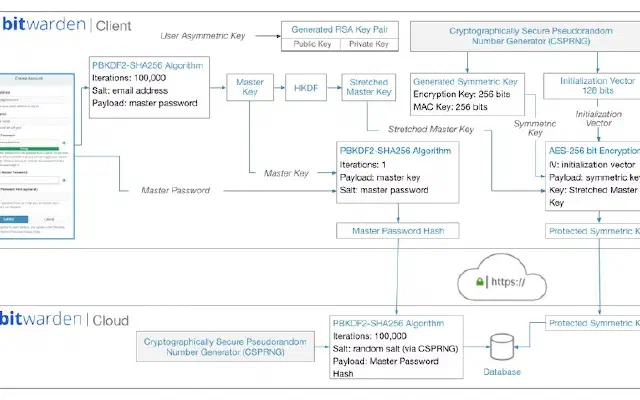
Bitwarden advertises 200,001 PBKDF2 iterations, twice LastPass. The 100,000 server-side rounds only protect the password hash, so an attacker with the vault skips them and tests guesses against the encryption key. Users can still drop to 5,000 iterations with no warning, and pre-2018 accounts started there. Bitwarden marketed a number that half of its own design ignores.